🧠 About ZeroDay Labs
Who We Are
ZeroDay Labs is an independent threat research outlet at the intersection of cybersecurity, emerging tech, and controlled chaos. We specialize in breaking down real-world exploits, dissecting malware campaigns, and exposing vulnerabilities—before they show up in your SIEM.
Whether it’s a brand-new CVE, a Telegram-born info-stealer, or a “legit” tool that suddenly starts dropping DLLs, we take it apart and turn it into something useful for defenders.
🔧 What We Do
-
Exploit & Malware Analysis
From zero-day PoCs to shady loaders, we reverse-engineer, validate, and translate technical threats into field-ready knowledge. -
Threat Intelligence Briefings
Fast, focused, and practical intel—complete with IOCs, Sigma/YARA rules, and notes on how attackers are really using the tools. -
Red Team R&D
We build emulation tools, custom C2 implants, and adversary simulations to keep detection teams sharp. -
Defender Enablement
Every article maps back to practical defense: hardened baselines, SOAR playbooks, WAF tuning, and threat-specific mitigations.
✍️ Why We Publish
Because good threat research shouldn’t be buried behind a paywall or a PowerPoint.
We believe in open, tactical reporting—free from fluff, full of copy-paste IOCs, and designed to help defenders take action faster. Transparency burns tools. That’s a win for the good guys.
👥 Meet the Team
Aidan Leon
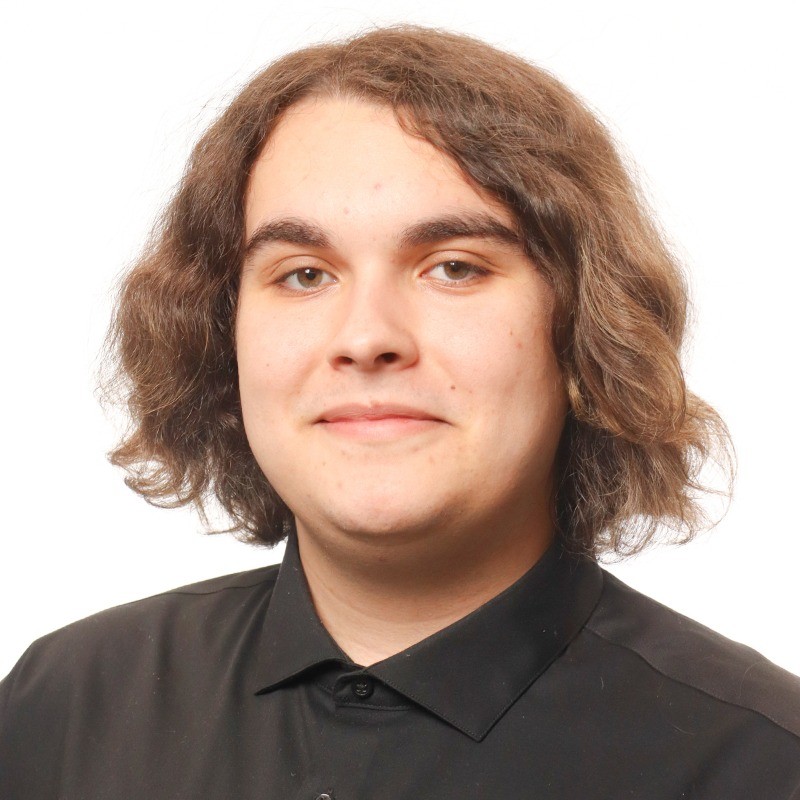
Founder, researcher, and caffeine-based lifeform. Currently a one-person SOC, fueled by curiosity, good coffee, and the occasional stack overflow. I specialize in reverse engineering, threat emulation, and making complicated attack chains readable.
Peanut
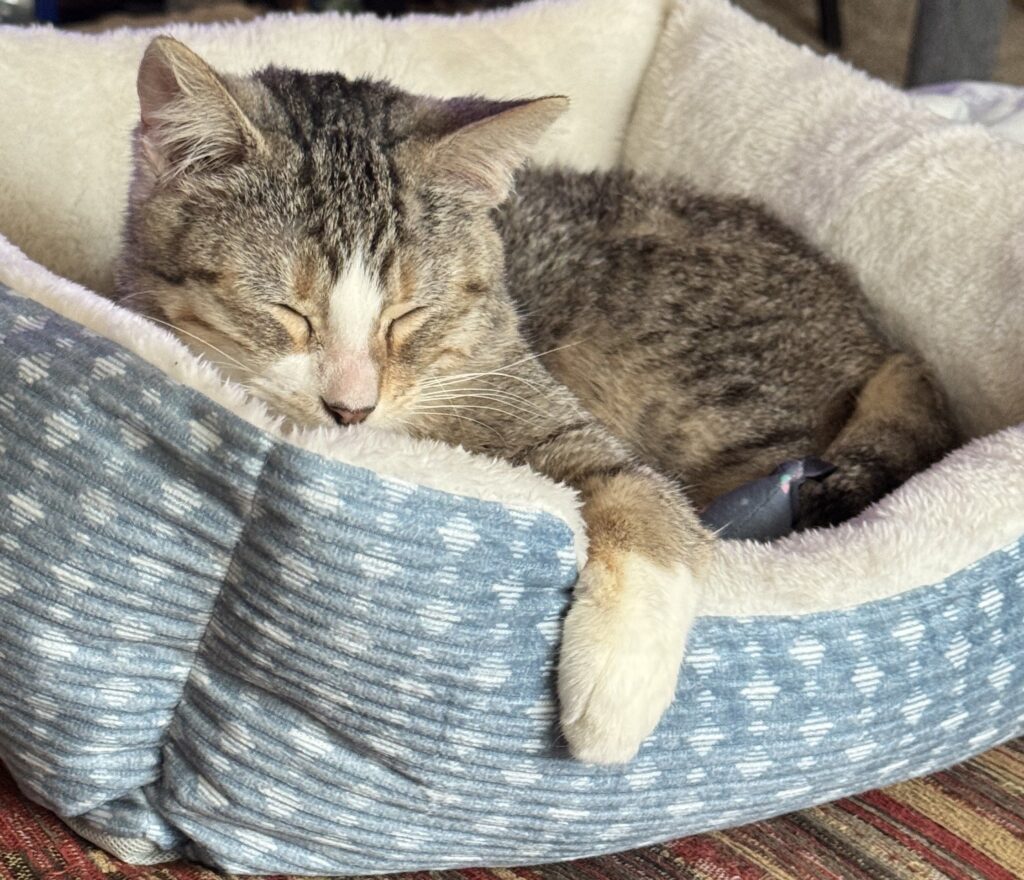
Senior cat. Mostly in charge of napping, sometimes keyboard interference. Not to be confused with the threat actor of the same name (though her persistence is comparable).
📡 Talk to us
Have an idea for a write-up?
A niche vulnerability that deserves more light?
Want to see a teardown of a firmware exploit or a wild malware sample? Drop us a line.
📬 Send concepts, samples, or napkin sketches to: [email protected]
Or ping us publicly via Linkedin (more methods coming soon)